Choice 01
No ban, but a secure alternative
A ban increases the risk of uncontrolled usage. Setting up a secure environment was therefore just as important as setting the rules.

What do you do as a municipality when your employees are using AI extensively without any terms or conditions? And how do you make sure that it happens responsibly and ethically?
Just like in other organisations, AI was being used extensively within the municipality. Policy officers had notes summarised by free chatbots, the communications team wrote texts using AI, and one team had even independently set up a tool that automatically sorted complaints. Each of these were good initiatives that contributed to improving service delivery, but they came with uncontrollable risks.
The CISO and the data protection officer identified the risks: confidential documents ending up outside the organisation, and applications that might be classified as high risk under the AI Act. As a management team you might be inclined to impose a (temporary) ban, but in reality that only increases the risk of further uncontrolled and unethical use.
To mitigate these risks, the municipality wanted a workable policy focused on security and ethics: managing the risks while giving employees the room to use AI responsibly.
Mapping actual usage, assessing every application for risk, and translating that into policy that is genuinely workable for employees.
A ban increases the risk of uncontrolled usage. Setting up a secure environment was therefore just as important as setting the rules.
The policy is written based on actual usage within the organisation, not on a theoretical picture of what employees might do.
The policy is structured around the identified risks. Applications are plotted within this framework rather than letting the application itself dictate terms.
To keep the implementation up to date, a regular scheduled moment is planned to evaluate new applications.
The framework the policy is built on
Unacceptable risknot permitted; the policy names these applications explicitly.
High riskonly after review. If residents are affected, the Algorithm Register comes first.
Limited riskpermitted, provided it is clear that AI is involved.
Minimal riskpermitted in the secure environment, with an internal record of purpose, data and owner.
Every application is plotted in this framework. The risk determines what is allowed, not the application itself.
clear vision on AI and how it is deployed.
Every organisation works with AI, but everyone does it differently.
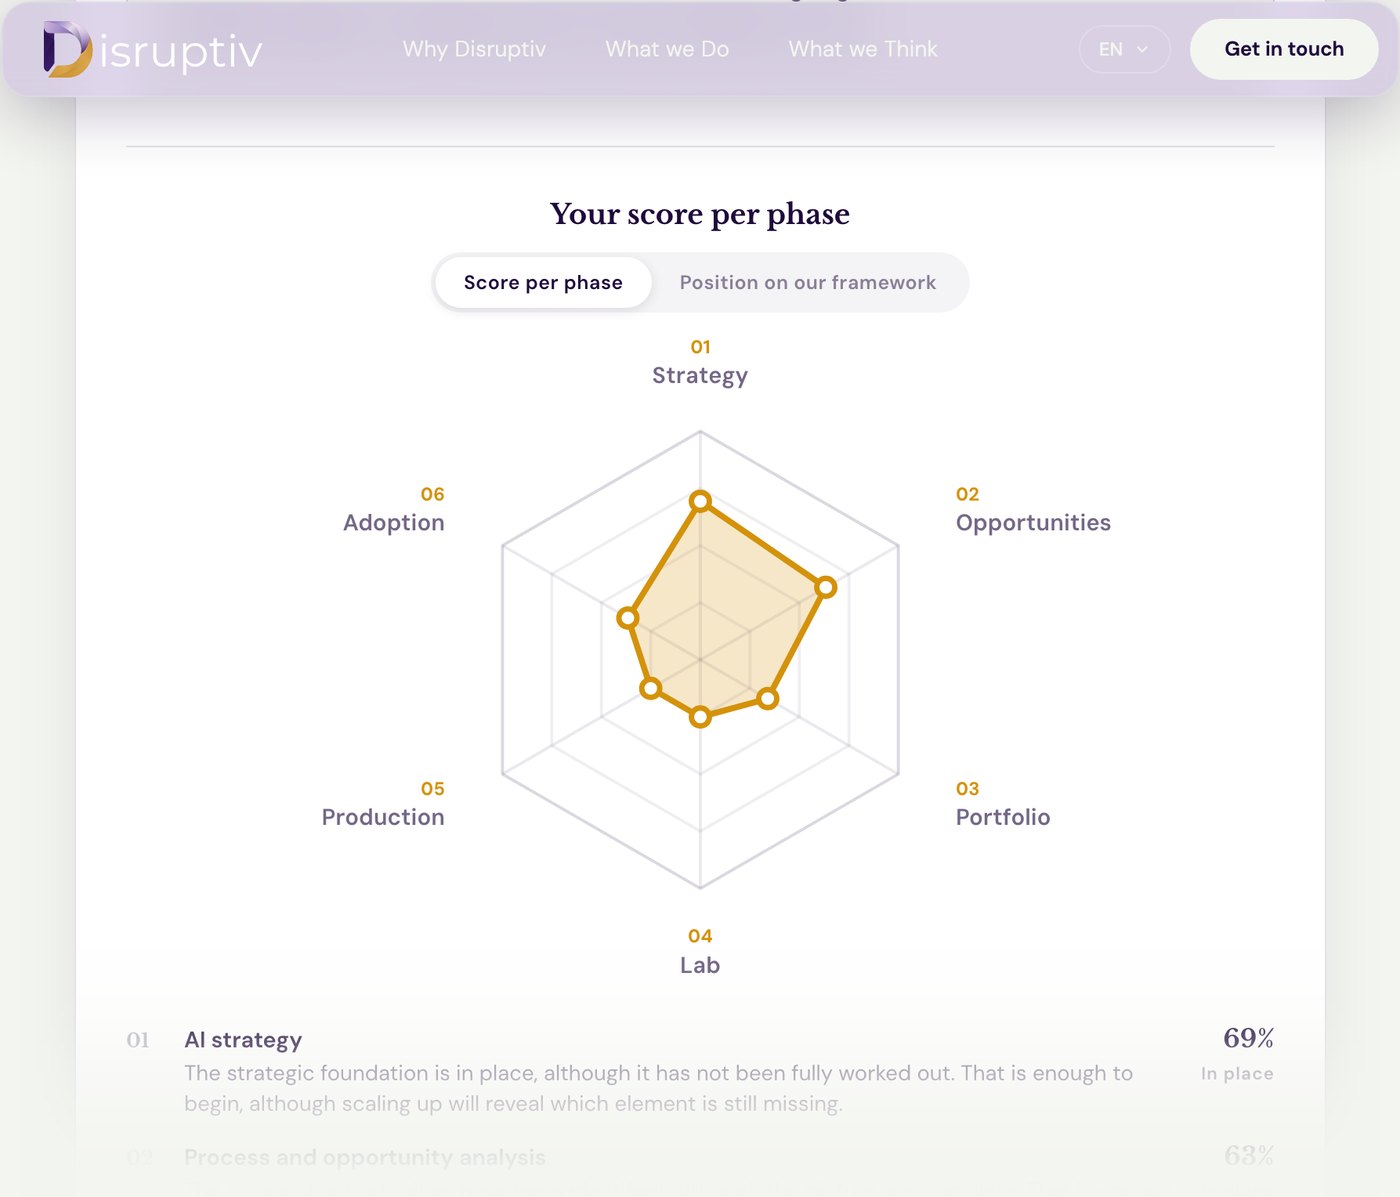
This case shows which phases of the Disruptiv framework another organisation went through. The assessment does the same for yours: you will not only see your score, but also which phase currently limits your progress and what needs to be done first.